Notes on building agents you can audit
What we’re learning about running AI agents against production systems — the architecture, the failure modes, and the things that turned out to matter more than we expected.
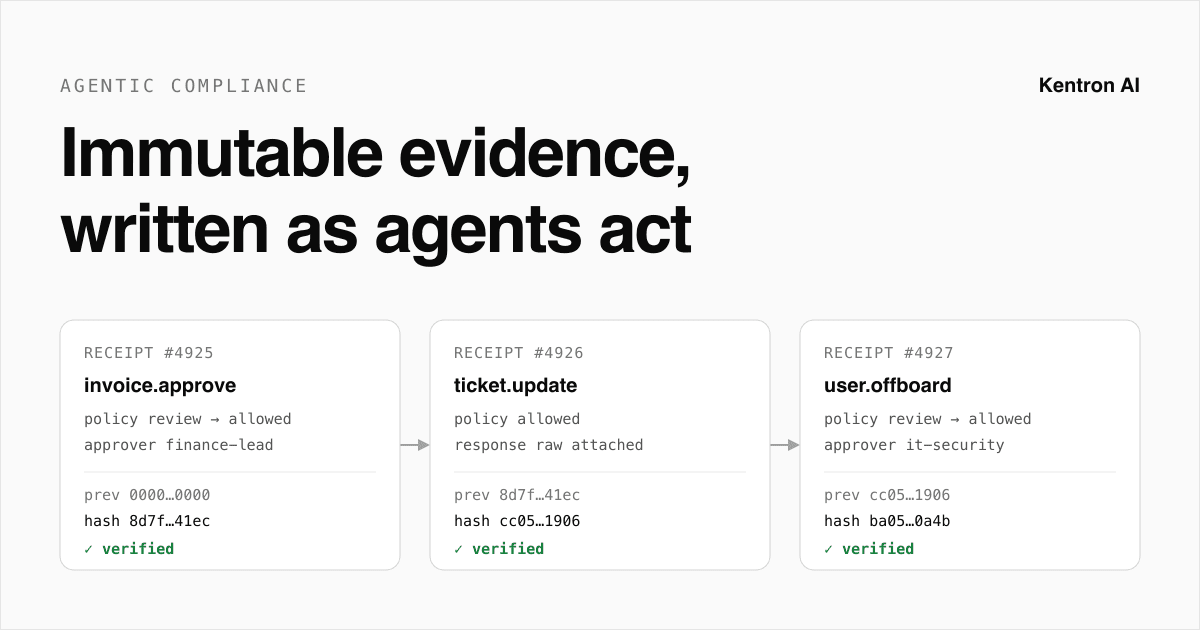
Agentic compliance runs on immutable evidence
Agentic compliance is the ability to prove, after the fact, that an AI agent did only what it was allowed to do. That proof has to be written at the moment the agent acts, and…
Read
The Future of Red Teaming: Adapting to Tomorrow's Threats
Red teaming continues to evolve alongside emerging technologies and threat landscapes. Several critical trends are shaping the discipline's future and redefining how organizations…
ReadPrompt Injection and Emerging Prompt-Based Attacks: What Security Teams Must Understand
Prompt injection has quickly become one of the most disruptive threats to modern AI systems. It doesn’t rely on breaking code or exploiting infrastructure. Instead, it manipulates…
Read
Red Teaming: The Art of Thinking Like an Adversary
In the ever-evolving landscape of cybersecurity, organizations face a critical challenge: how do you truly know if your defenses will hold when facing a determined, sophisticated…
Read
AI Model Security: Beyond the Hype to Real-World Resilience
As organizations rush to integrate Large Language Models (LLMs) into critical business operations, a sobering reality emerges: finding genuinely secure, trustworthy, and…
Read
Why Guardrails Are the Essential Shield for AI Agents in 2025
AI agents are rapidly moving from prototypes to production. They now handle customer service, automate recruiting, draft emails, and process internal data. But this autonomy comes…
Read
Want the short version? See what Kentron AI actually does